If you are giving AI agents real tools—file editors, shell access, API clients—you need to think about what happens when those tools get used. Model Context Protocol is becoming a common way for AI agents to connect to tools, files, APIs and developer workflows. That is useful, but it creates a new operational question: what happens when an agent can call real tools and change real systems?
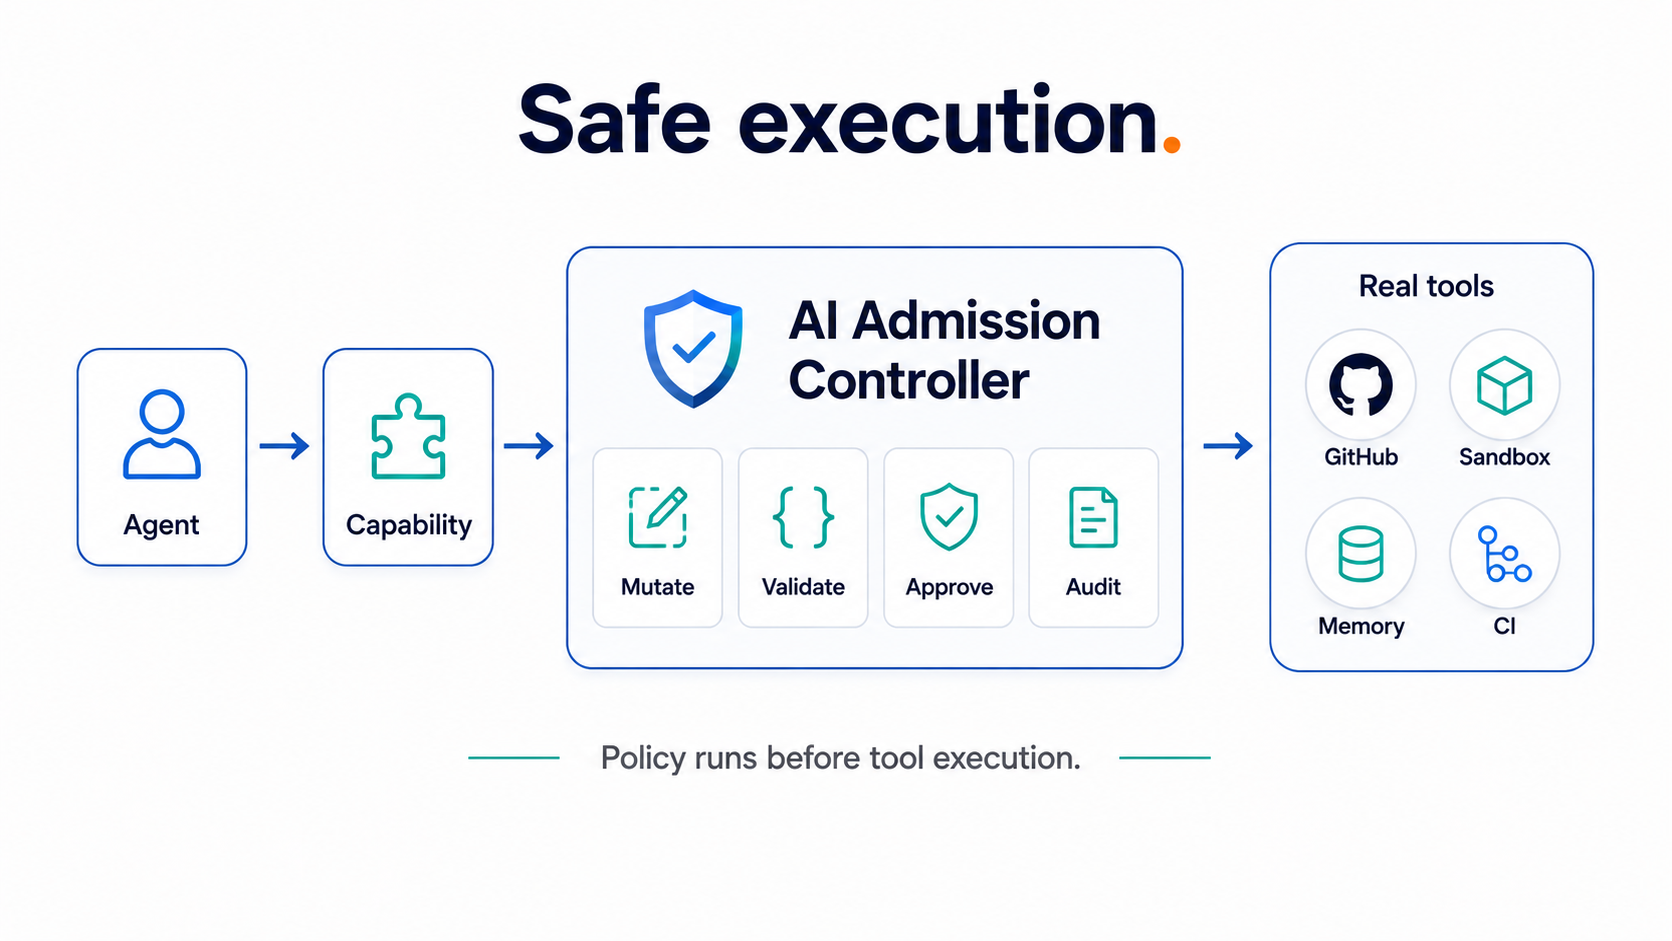
MCP security is not only about server authentication or network transport. The hard part is deciding whether a specific tool-call is safe in its current context. A read-only lookup, a file edit, a pull request, a shell command and a deploy should not be treated as the same class of action.
What MCP security means in practice
- Tool discovery control: which tools are visible to which agent, project or user.
- Tool-call validation: whether a specific set of arguments is allowed.
- Safe mutation: adding defaults such as
draft=true,dry_run=trueor a branch prefix. - Audit: recording who asked, which agent acted, which tool was called and what changed.
- Prompt hygiene: making sure instructions do not live only in fragile prompt text.
The key shift: AI security moves from “is this API endpoint protected?” to “is this tool-call safe for this agent, user, repo and task?”
Why prompts are not enough
You can tell an agent to be careful. You can write a system prompt that says not to touch production, not to edit secrets and not to open a pull request without tests. But prompts are advisory. Policies are enforceable.
Where Actlane fits
Actlane is designed for teams that do not want safety rules scattered across prompts, MCP config files, OpenAPI definitions and custom gateway code. It defines a capability once and generates surrounding integration and policy artifacts.
capability.yaml
  → MCP tool schema
  → OpenAPI Action
  → IDE / agent config
  → policy bundle
  → audit metadata
Example: safe pull request creation
Instead of exposing low-level tools such as github.create_branch, github.commit_files and github.create_pull_request directly, expose a high-level capability: create_safe_draft_pr.
Bottom line
MCP connects agents to tools. MCP security is about making those connections safe, predictable and auditable. The missing layer is a reusable action contract that travels across agent runtimes.
Why this topic is related to Actlane
MCP security is not only about connecting to servers; it is about deciding whether each tool call is safe. Actlane defines the contract around a tool call: schema, prompt hints, policy, safe defaults and audit metadata.
Try Actlane
Actlane is a DSL-first toolkit for safe AI-agent actions. It defines what each tool-call should do, generates safe defaults, policy rules and audit metadata—all from a single capability manifest.
Explore on GitHub · See the safe draft PR example · Back to all articles